Key takeaways
- Threat detection and response means finding attacks early and acting on them before they cause damage.
- You spot threats early by combining four methods: indicator matching, behavioural detection, anomaly detection and threat hunting.
- The earliest signs often appear in identity and email (unusual sign-ins, new inbox rules, unexpected app consents), not only on devices.
- After detection comes contain, remove, recover and verify, and a written agreement decides who is allowed to act.
- Microsoft Defender XDR documents 13 automatic response actions, some still in preview, and they only run with qualifying licences and the right settings.
- Measure threat detection and response by speed, accuracy and coverage.
Threat detection and response (TDR) is the continuous practice of finding malicious activity across endpoints, identities, email and cloud, then containing, removing and recovering from it before an attacker reaches their goal. This guide covers the warning signs to watch, the response steps that follow, and what Microsoft Defender can stop automatically. Automation can contain an attack, but people still have to investigate, remediate and restore.
What Is Threat Detection and Response (TDR)?
Threat detection and response (TDR) is the continuous practice of finding malicious activity across endpoints, identities, email and cloud, then containing, removing and recovering from it before an attacker reaches their goal.
Detection and response only work as a pair. Detection without response produces alerts nobody acts on, and response without detection only catches what users report. Both halves need round-the-clock coverage, so it helps to know what continuous 24/7 threat monitoring includes.
Threat Detection vs Threat Response: What's the Difference?
Threat detection finds and confirms malicious activity. Threat response stops it and restores normal operations.
How Does Threat Detection and Response Work?
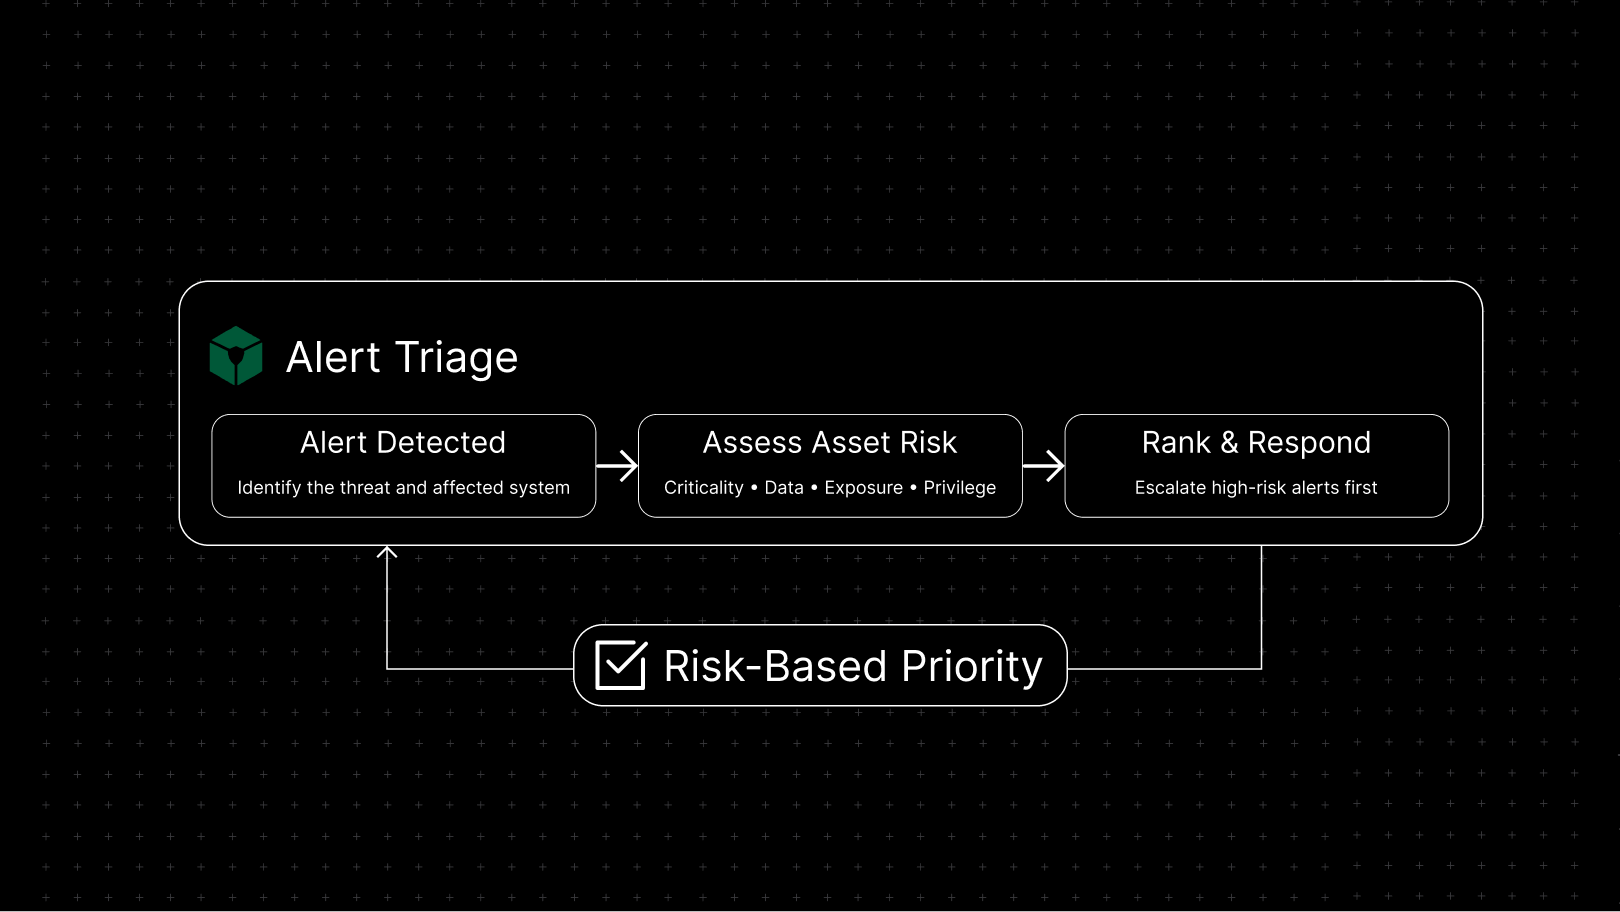
Threat detection and response runs as a continuous loop: collect telemetry, detect, investigate, contain, then remediate and feed what you learn back into detection.
- Collect telemetry. Sign-in, email, endpoint, cloud and network logs flow into one place, such as Microsoft Sentinel and Microsoft Defender XDR. Output: a searchable record of what happened, where and when.
- Detect. Analytics rules, behavioral models and threat intelligence flag activity that matches an attack pattern or breaks from normal. Output: alerts, grouped into a single incident when they share an attacker.
- Investigate. An analyst confirms the incident is real, works out what the attacker touched and sets its priority. Output: a confirmed, scoped incident, or a closed false positive.
- Contain. Responders or automated actions isolate devices, disable accounts and revoke sessions. Output: an attacker who can no longer move or act.
- Remediate and improve. The team removes persistence, resets credentials, restores systems, then tunes detections to catch what was missed. Output: a clean environment and sharper detection next time.
How TDR Fits NIST's Current Incident Response Guidance
The National Institute of Standards and Technology (NIST) published SP 800-61 Rev. 3 in April 2025, superseding Rev. 2 from 2012. It replaces Rev. 2's four-phase incident response lifecycle with a model built on the six NIST Cybersecurity Framework (CSF) 2.0 functions. Govern, Identify and Protect prepare for incidents, while Detect, Respond and Recover handle them. Lessons feed back through the Improvement category of Identify. NIST also says organizations should use whichever lifecycle model suits them best.
How to Spot Cyber Threats Before They Cause Damage
You spot cyber threats early by watching identity, email, endpoint, cloud and network activity for known-bad indicators and abnormal behavior, then investigating anything that matches a real attack pattern.
The 4 Cyber Threat Detection Methods
No single detection method catches everything, so security teams layer four of them.
- Indicator matching: Checks activity against indicators of compromise (IOCs), such as known-bad IP addresses, domains and file hashes. Catches: repeat attacks. Misses: new or rotated attacker infrastructure.
- Behavioral detection: Flags indicators of attack (IOAs), meaning attacker techniques mapped to MITRE ATT&CK. Catches: new tools using known techniques. Misses: techniques no one has written a detection for.
- Anomaly detection: User and entity behavior analytics (UEBA) flags departures from normal activity. Catches: misuse of valid accounts. Misses: attackers who blend in, and it raises more false alarms.
- Threat hunting: Analysts test hypotheses to find attackers that automated detection missed. Catches: stealthy, hands-on intrusions. Misses: anything outside the hunts that analyst time allows.
For how the first two differ in practice, see the difference between IOCs and IOAs.
Early Warning Signs of an Active Attack
Early warning signs often appear in identity and email activity, not only on devices.
Not every warning sign is an attack. In a CyberQuell investigation of suspicious Microsoft 365 sign-ins, the unusual-location alerts traced back to network routing, and no account was compromised.
Where Threats Show Up: Detection Coverage by Attack Surface
Each attack surface needs its own detection source, and in a Microsoft environment most of them map to a Defender product.
What Happens After a Threat Is Detected?
Once a threat is confirmed, responders contain it, remove what the attacker left behind, recover affected systems and check the attacker is gone. Your contract decides who does each step.
Containment, Removal and Recovery Actions
Each stage has different actions, a different chance of undoing them, and a different owner.
Who Is Allowed to Act? Three Response-Authority Models
NIST SP 800-61 Rev. 3 says your provider contract should define the provider's authority to act on your behalf, and what it may not decide alone.
- Pre-authorized. The provider contains threats immediately, within agreed limits. This is the fastest model.
- Approval-required. The provider recommends an action, then waits for a named person to approve it. This is slower out of hours.
- Notify-only. The provider alerts you, and your team contains the threat.
Whichever model you choose, the agreement should define:
- actions taken automatically
- actions that need approval, and who approves out of hours
- how quickly you are notified
- systems that may be isolated, and those that may not
- who patches, rebuilds and resets credentials
- who preserves evidence, and for how long
- what counts as closed
For contract wording, see which response decisions stay with you when you outsource.
How to Confirm Remediation Worked
Remediation has worked only when every access path is closed and the attacker doesn't return. A password reset alone doesn't prove that.
- No indicators of compromise remain on affected systems or other likely targets.
- No persistence remains: inbox rules, OAuth app consents, scheduled tasks or unknown accounts.
- Credentials are reset and active sessions are revoked.
- The root cause is fixed.
- No attacker activity returns during an agreed watch period.
Then declare the incident closed and report it to leadership, following how to report a live incident to executives.
What Can Microsoft Defender Stop Automatically, and What Still Needs a Human?
With qualifying licenses and settings, automatic attack disruption in Microsoft Defender XDR can contain devices, users and IP addresses, revoke sessions and act on compromised OAuth apps during an attack. Microsoft leaves investigating, remediating and bringing assets back online to your security team.
The 13 Automatic Response Actions in Microsoft Defender
Microsoft documents 13 automatic response actions across Defender, Microsoft Entra ID and Microsoft Sentinel.
By product: Defender for Endpoint 7, Entra ID 2, Sentinel connectors 2, Defender for Identity 1, Defender for Cloud Apps 1.
By capability: 9 attack disruption only, 3 predictive shielding only, 1 both.
For containment actions, Defender requires detector confidence of 99% or higher. Your team can undo every automatic action, and you can exclude critical users, devices and IP addresses.
Licenses and Settings Required for Automatic Attack Disruption
Attack disruption runs only when you hold a qualifying subscription and each product's prerequisites are in place.
Qualifying subscriptions include:
- Microsoft 365 Business Premium, through its included Defender for Business, which contains compromised devices and their user accounts
- Microsoft 365 E5 or A5
- Microsoft 365 E3 with the Microsoft Defender Suite or Enterprise Mobility + Security (EMS) E5 add-on, or A3 with the A5 Security add-on
- Office 365 E5 or A5, Windows 10/11 Enterprise E5 or A5, or EMS E5 or A5
- Standalone Defender for Endpoint Plan 2, Defender for Identity, Defender for Cloud Apps or Defender for Office 365 Plan 2
Settings to check:
- Defender for Endpoint: device discovery set to Standard (needed for Contain device), device group remediation level set to Full or Semi, Sense agent v10.8470 or later (needed for Contain user)
- Defender for Identity: sensor and auditing on domain controllers, action accounts validated
- Defender for Cloud Apps: Microsoft 365 connector with every checkbox selected, including Microsoft Entra ID apps
- Defender for Office 365: mailboxes in Exchange Online, auditing MailItemsAccessed, UpdateInboxRules, MoveToDeletedItems, SoftDelete and HardDelete
- AWS and Okta actions: Microsoft Sentinel workspace connected to the unified security operations portal
What Automation Does vs What Your SOC Still Owns
Defender contains the attack; your SOC or managed detection and response (MDR) provider still finishes it.
For the wider limits of automation, see what SOC automation still can't handle.
Actions, statuses and prerequisites verified against Microsoft Learn's automatic attack disruption, predictive shielding and configuration pages on 17 September, 2026. Preview features change.
If you're not sure your licenses and settings let attack disruption run, talk to CyberQuell's managed XDR team in a free 15-minute consultation.
Real Example: A BEC Attack That Survived a Password Reset
In a CyberQuell investigation, an attacker kept access to a Microsoft 365 mailbox at a professional services firm of about 50 employees for four months, even after a password reset and session revocation. The reset missed the persistence: likely a malicious OAuth app with delegated mailbox permissions, which password changes don't revoke.
The investigation steps and full remediation list are in the full BEC case study.
How Do You Measure Threat Detection and Response?
Measure threat detection and response on three things: speed (how fast you detect, acknowledge and contain), accuracy (how many alerts are real) and coverage (how much of the estate is monitored).
Speed and automation both show up in breach costs. IBM's Cost of a Data Breach Report 2026 puts the global average breach at $4.99 million, up 12% and a record high. Organizations using security AI and automation extensively saved $1.93 million compared with organizations using none.
Final Thoughts
Threat detection and response only protects a business when three things work together. You need visibility into identity and email as well as devices. Containment has to start without waiting for someone to wake up. And it must be clear who finishes the job once the attacker is contained. The last two are the ones that fail quietly, because nothing raises an alert when attack disruption is misconfigured or when a response agreement was never written down.
Book a call with CyberQuell to find out whether attack disruption is actually running in your Microsoft environment and who is authorized to act on an alert at 3 a.m. We'll also look at where 24/7 SOC monitoring and response, backed by a 15-minute response SLA, would close the gaps that call uncovers.