Key Takeaways
- SOC 2 is an attestation report issued by an independent certified public accountant (CPA) firm, not a certification.
- Type 1 checks control design at one point in time, while Type 2 tests whether controls operated effectively over a period, usually 3 to 12 months.
- Logical access (CC6) and system operations (CC7) are the Common Criteria that rely most on continuous security monitoring.
- Auditors want proof that monitoring ran and alerts were acted on all period, not just that tools were configured.
- Microsoft's own SOC 2 reports cover Microsoft's controls, not the ones you operate in Microsoft 365 and Azure.
A System and Organization Controls 2 (SOC 2) Type 2 audit tests whether your security controls operated throughout a set period, not just whether they exist. In our experience, most audit exceptions land in monitoring and incident response, because those are the controls that have to run every day of the observation window. This guide covers which Trust Services Criteria depend on continuous monitoring, what evidence auditors expect, and how Microsoft Sentinel produces it.
What Is SOC 2 Type 2?
SOC 2 Type 2 is an attestation report in which an independent certified public accountant (CPA) firm tests whether a service organisation's security controls operated effectively over a defined period. The benchmark for a SOC 2 Type 2 examination is the Trust Services Criteria, published by the American Institute of Certified Public Accountants (AICPA).
The Trust Services Criteria cover five categories:
- Security, required in every SOC 2 report
- Availability, optional
- Processing integrity, optional
- Confidentiality, optional
- Privacy, optional
The organisation picks which optional categories to include, based on what it commits to its customers. The AICPA's SOC 2 guidance sets out the current criteria.
Enterprise customers usually ask for a SOC 2 Type 2 report during vendor due diligence, before they sign or renew a contract with a provider that will handle their data. Buyers prefer Type 2 over Type 1 because it shows controls working across months, not just designed on paper.
SOC 2 Type 2 is also written as SOC 2 Type II, and sometimes shortened to SOC Type 2. All three names refer to the same report.
SOC 2 Type 1 vs Type 2: What's the Difference?
A SOC 2 Type 1 report assesses whether controls are designed properly at a single date. A SOC 2 Type 2 report tests whether controls were designed properly and also operated effectively across an observation period.
The AICPA does not fix the length of the observation period. Compliance platform Secureframe notes that the standard only requires a period long enough to show operating effectiveness. Many auditors start with a 3-month window, then move to 12 months.
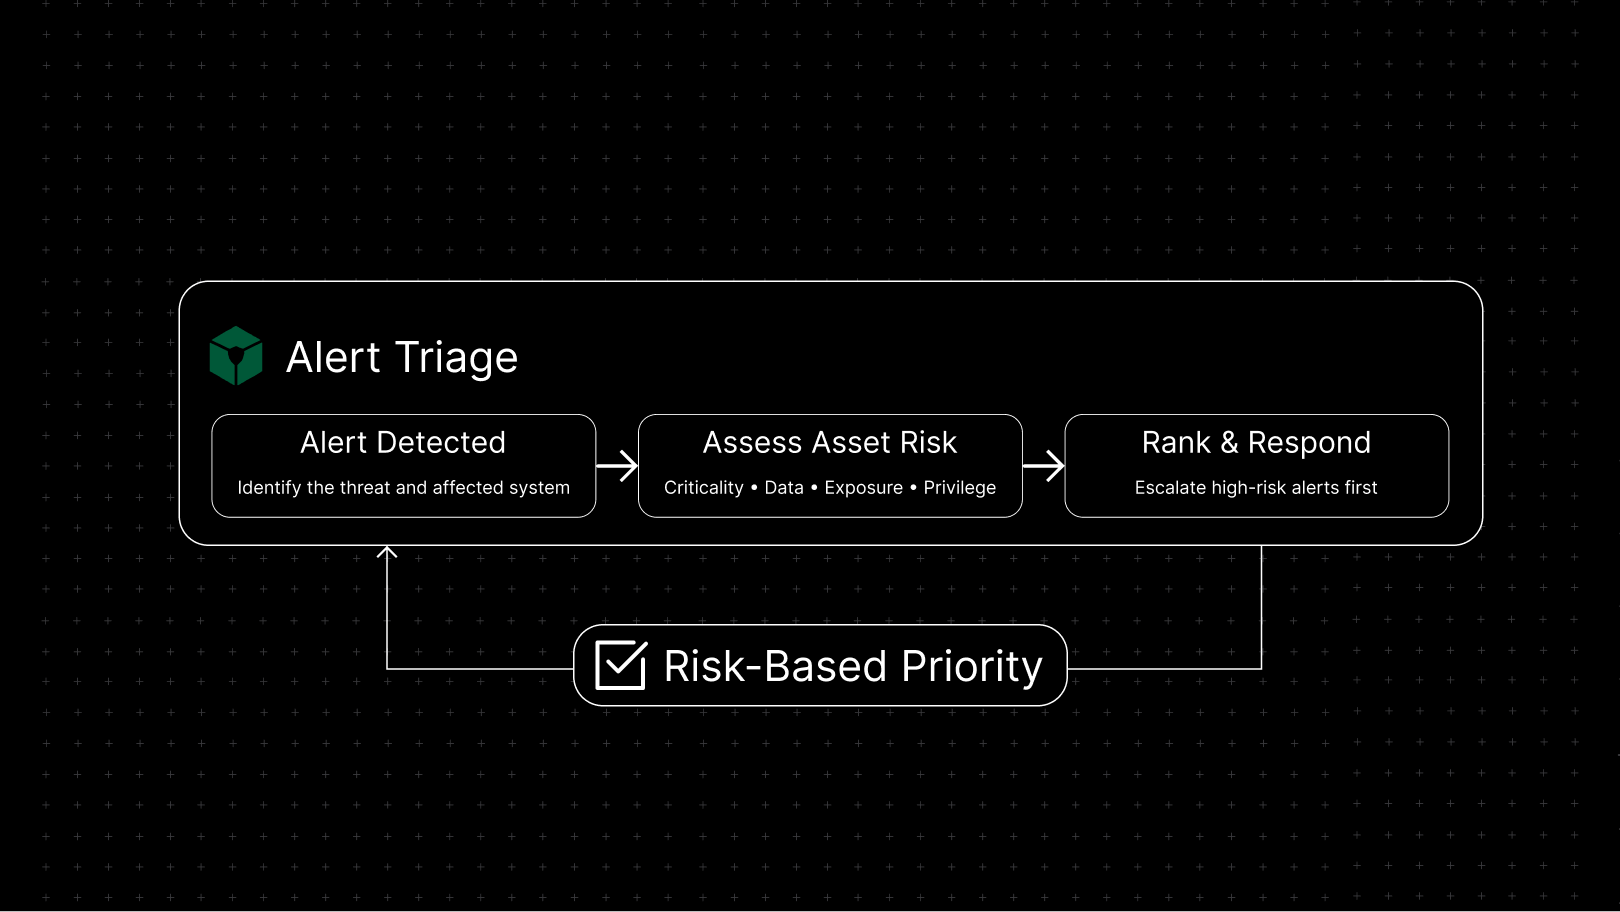
The monitoring row is where most organisations feel the difference. For Type 1, a configured Microsoft Sentinel workspace with active analytics rules can show the design is in place. For Type 2, the auditor samples alerts from across the window and checks that each one was triaged, investigated or closed with a documented reason.
Preparing for a SOC 2 Type 2 observation window? Before the window opens, a security assessment of your Microsoft 365 and Azure logging shows whether your monitoring will produce the evidence an auditor asks for. It is a readiness check, not an audit.
Which SOC 2 Criteria Depend on Security Monitoring?
The SOC 2 controls that depend most on security monitoring fall under CC6 (logical and physical access controls) and CC7 (system operations). CC7 covers detecting anomalies, evaluating security events, responding to incidents and recovering from them.
CC6 and CC7 both sit within the Common Criteria. Every SOC 2 report must meet the Common Criteria, because together they make up the mandatory Security category. CC4 (monitoring activities) sounds related but covers something different: whether management checks that its controls are working, not security event monitoring. The wording below is summarised from the AICPA's 2017 Trust Services Criteria (with revised points of focus, 2022).
Logs only count as evidence if they still exist when the auditor asks for them. Microsoft Entra ID keeps sign-in and audit logs for 30 days with a P1 or P2 licence, and seven days on the free tier. A 12-month observation window therefore needs those logs routed to Microsoft Sentinel or long-term storage from the first day. Logs that expire before they are archived cannot be recovered.
What Evidence Do SOC 2 Type 2 Auditors Expect From Security Monitoring?
SOC 2 Type 2 auditors expect proof that security monitoring ran throughout the observation period and that alerts were reviewed and acted on. Screenshots of tool configuration only show that monitoring was set up. That answers a Type 1 question, not a Type 2 one.
Auditors usually test this by sampling records from across the whole window. SOC 2 evidence collection for security monitoring typically covers seven areas:
- Log-source coverage. A list of in-scope systems, with proof that each one sent logs to the SIEM (security information and event management) system for the whole period, including any gaps and how they were fixed.
- Detection rules and their change history. The analytics rules that were active, plus who changed them, when and why.
- Alert triage records. For sampled alerts, who reviewed each one, when, and why it was escalated or closed.
- Incident tickets. Detection time, analyst actions, containment steps and resolution, recorded as they happened rather than written up afterwards.
- Post-incident reviews. Root cause, lessons learned and the changes made afterwards, showing that a documented incident response process was followed.
- Periodic access reviews. Proof that user and admin access was reviewed on the schedule your own policy sets.
- Vulnerability scan cadence. Scan results at the frequency your policy commits to, with fixes tracked against your own deadlines.
How Long Should Logs Be Kept for SOC 2?
The AICPA does not set a fixed log retention period for SOC 2. Retention has to cover at least the full observation window. Many organisations keep logs for 12 months, which compliance platform Secureframe describes as an industry standard rather than a SOC 2 requirement.
Microsoft 365 does not keep identity logs that long by default. Microsoft Entra ID retains sign-in and audit logs for 30 days on P1 or P2, and seven days on the free tier. Route them to Microsoft Sentinel or long-term storage before the observation window opens, because logs that expire before they are archived cannot be recovered.
How Microsoft Sentinel and Defender Support SOC 2 Type 2 Evidence
Microsoft Sentinel centralises security logs and records every incident with timestamps. Microsoft Defender XDR (extended detection and response) and Microsoft Entra ID generate the detection and access records that SOC 2 auditors sample. These tools only produce usable evidence if someone reviews and acts on their alerts every day of the observation period.
Each tool maps to specific criteria:
- Microsoft Sentinel analytics rules and incidents (CC7.2 to CC7.4). Analytics rules raise alerts on anomalies. Each incident keeps an owner, status history, comments and closure reason, which together form the triage and response trail that auditors test.
- Microsoft Sentinel workbooks (periodic reporting). Workbooks turn the same log data into recurring reports, such as monthly incident volumes and time to close. Microsoft publishes a list of commonly used workbooks, but none is built for SOC 2, so reports are shaped around your own controls.
- Microsoft Defender for Endpoint (CC6.8). Records malware detections and the remediation taken on each device.
- Microsoft Entra ID sign-in and audit logs (CC6). Show who signed in, from where, and every change to users, groups and roles.
- Microsoft Purview Compliance Manager. Offers a premium SOC 2 assessment template that maps the criteria to improvement actions in your tenant. See how Compliance Manager works.
Microsoft's SOC 2 Report Does Not Cover Your Controls
Microsoft publishes SOC 2 Type 2 reports covering Azure, Office 365, Microsoft Defender XDR, Microsoft Defender for Endpoint and Microsoft Intune, among other services. Each report ends with a list of user entity responsibilities: the controls customers must operate themselves for the whole system to meet SOC 2.
Using Microsoft 365 does not make your company SOC 2 compliant. Before the observation window opens, check which controls stay yours when you outsource. For most 50 to 500 person companies, managed Microsoft Sentinel monitoring is how the daily review actually gets done.
Can a Managed SOC Help You Pass a SOC 2 Type 2 Audit?
A managed security operations center (SOC) can run your monitoring and incident response controls and produce the evidence SOC 2 auditors sample. A managed SOC cannot issue the SOC 2 report or take ownership of your controls. Only a licensed CPA firm can issue the report, and the controls remain your organisation's responsibility.
The two acronyms are unrelated. A SOC is a security team. SOC 2 stands for System and Organization Controls 2, the AICPA reporting framework.
Why part-time coverage creates gaps. A Type 2 audit samples records from the whole window, including nights, weekends and holidays. An alert raised at 2 a.m. on a Saturday and left until Monday is still in the sample, and a 48-hour gap in triage is hard to present as a control that operated effectively. This is why part-time SOC coverage fails compliance, and why 24/7 managed SOC monitoring and response is the usual answer for companies without their own night shift.
How auditors treat your provider. A managed SOC is a vendor, so it falls under criterion CC9.2, which covers assessing and managing risks from vendors and business partners. Expect the auditor to ask how you selected and oversee the provider, and possibly for the provider's own SOC 2 report.
What stays with you. Security policies, access approvals, risk assessment and decisions on how to act during an incident all remain with your organisation. The provider runs the monitoring, and you stay accountable for the controls.
SOC 2 Type 2 Monitoring Checklist
This SOC 2 compliance checklist for security monitoring sets out eight steps that make security monitoring audit-ready before the observation window opens. It covers monitoring and incident response controls only, not full SOC 2 readiness areas such as policies, HR controls or vendor management.
- Define in-scope systems. List every system in your SOC 2 system description, so monitoring coverage can be checked against it.
- Connect all log sources. Send Microsoft Entra ID, Microsoft Defender XDR, Office 365 and Azure activity logs to Microsoft Sentinel, and set an alert for any source that stops sending data.
- Set retention to cover the window. Keep logs for at least the full observation period, or longer if your own policy says so.
- Enable and document detection rules. Record which analytics rules are active, what each one detects, and every change made during the window.
- Define triage service level agreements (SLAs). Set how quickly alerts of each severity must be reviewed, then measure against those targets. An SLA written around business hours leaves nights and weekends uncovered, which is the gap 24/7 threat monitoring closes.
- Ticket every incident. Record detection time, owner, actions taken and resolution, including alerts closed as false positives.
- Run and record access reviews. Review user and admin access on the schedule your policy sets, and keep the sign-off.
- Produce monthly evidence reports. Export incident counts, triage times and log-source health each month, so the evidence exists before the auditor asks for it.
Final Thoughts
For security monitoring, a SOC 2 Type 2 audit tests one thing: whether it ran every day of the observation window, and whether you can prove it. Tools like Microsoft Sentinel make the proof possible. The harder part is the daily review and the documented response.
Book a call with CyberQuell to plan the monitoring and incident response side of your observation window on Microsoft Sentinel. Our 24/7 managed SOC monitoring and response produces the evidence your auditor will sample.